
The engineering behind zero-knowledge security
Deep dives into the encryption, key hierarchy, authentication and abuse-protection that make PulsVault a fully secure platform — written by the people who build it.
PulsVault Security Team
Security & Cryptography
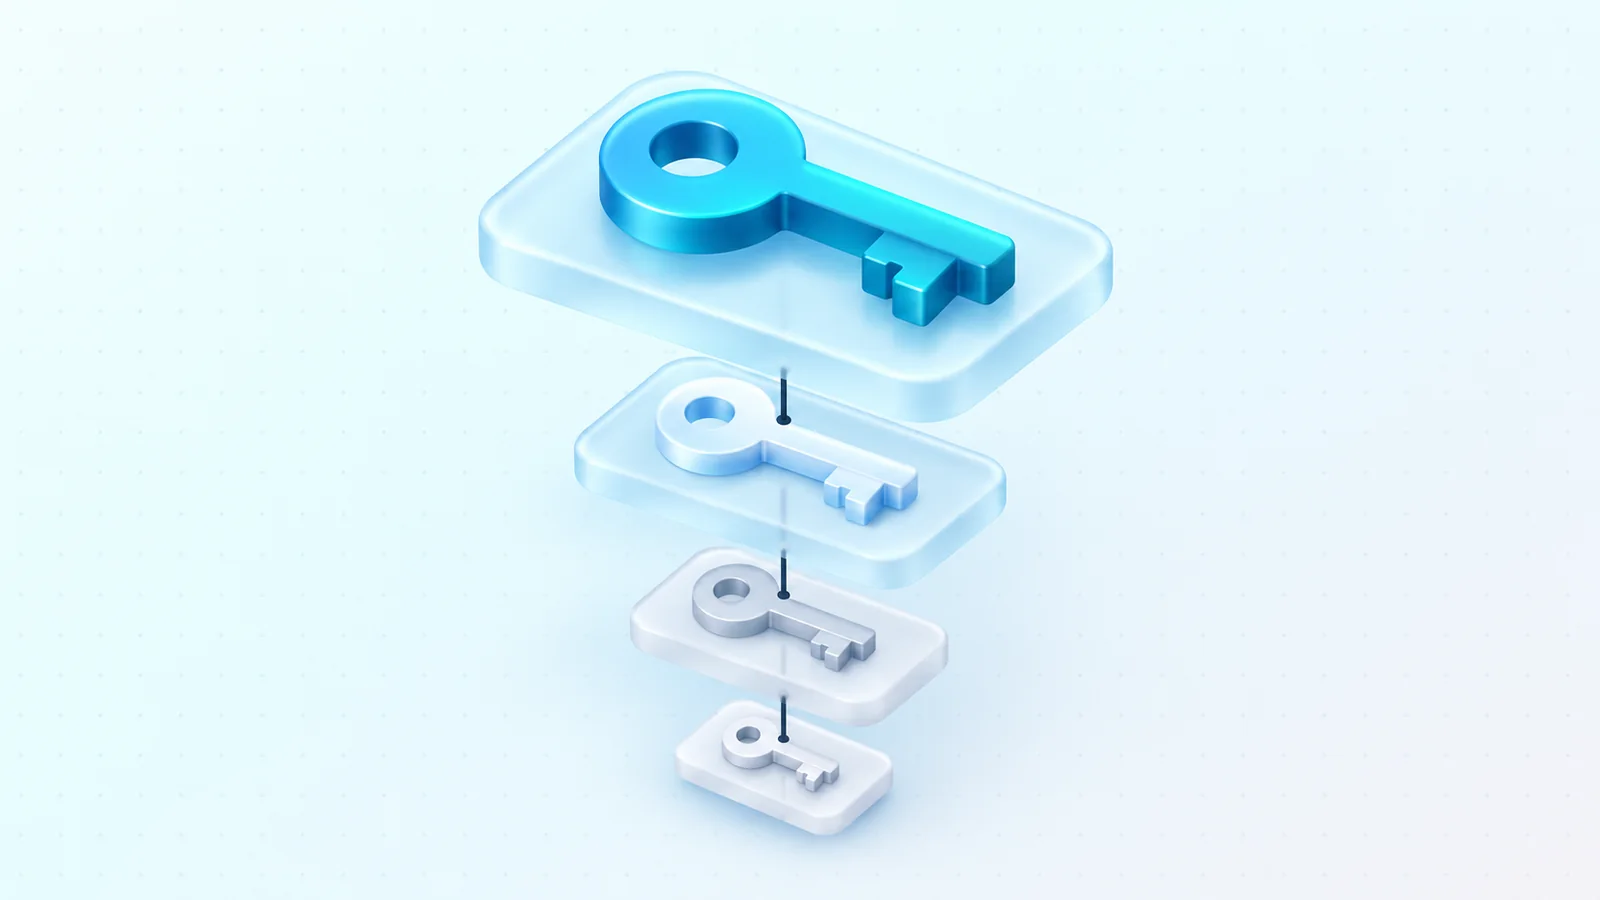
The Key Hierarchy: PDS → KEK → UMK → DEK
A single layered chain of keys is what lets you change a password without re-encrypting your whole vault. Here is how the chain is built.
PulsVault Security Team
06/23/2026
AES-256-GCM: Our Primary Vault Cipher
Why authenticated encryption is non-negotiable, and why the primary vault is always AES-256-GCM and never shareable.
PulsVault Security Team
06/22/2026
Unique 12-Byte IVs: Never Reuse a Nonce
Nonce reuse is the classic way to break GCM. We generate a fresh 12-byte IV for every single encryption — here is why it matters.
PulsVault Security Team
06/21/2026
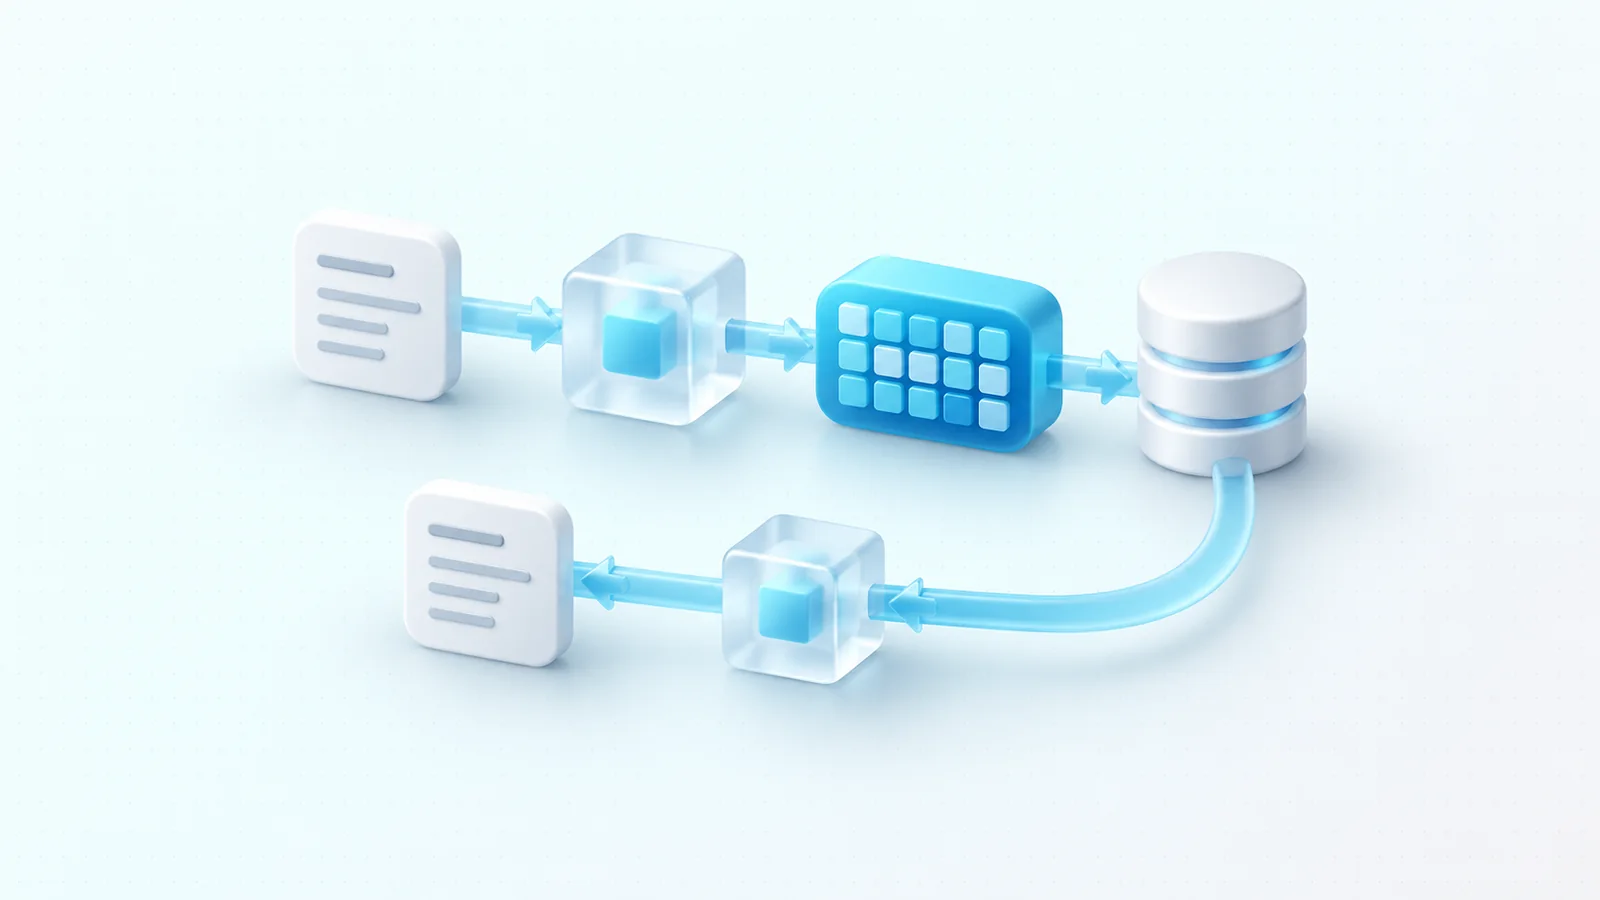
Inside the Encryption / Decryption Pipeline
Follow a single password field from the moment you type it to the moment it is read back — entirely on your device.
PulsVault Security Team
06/20/2026